Encryption is Not Free—Especially at Scale
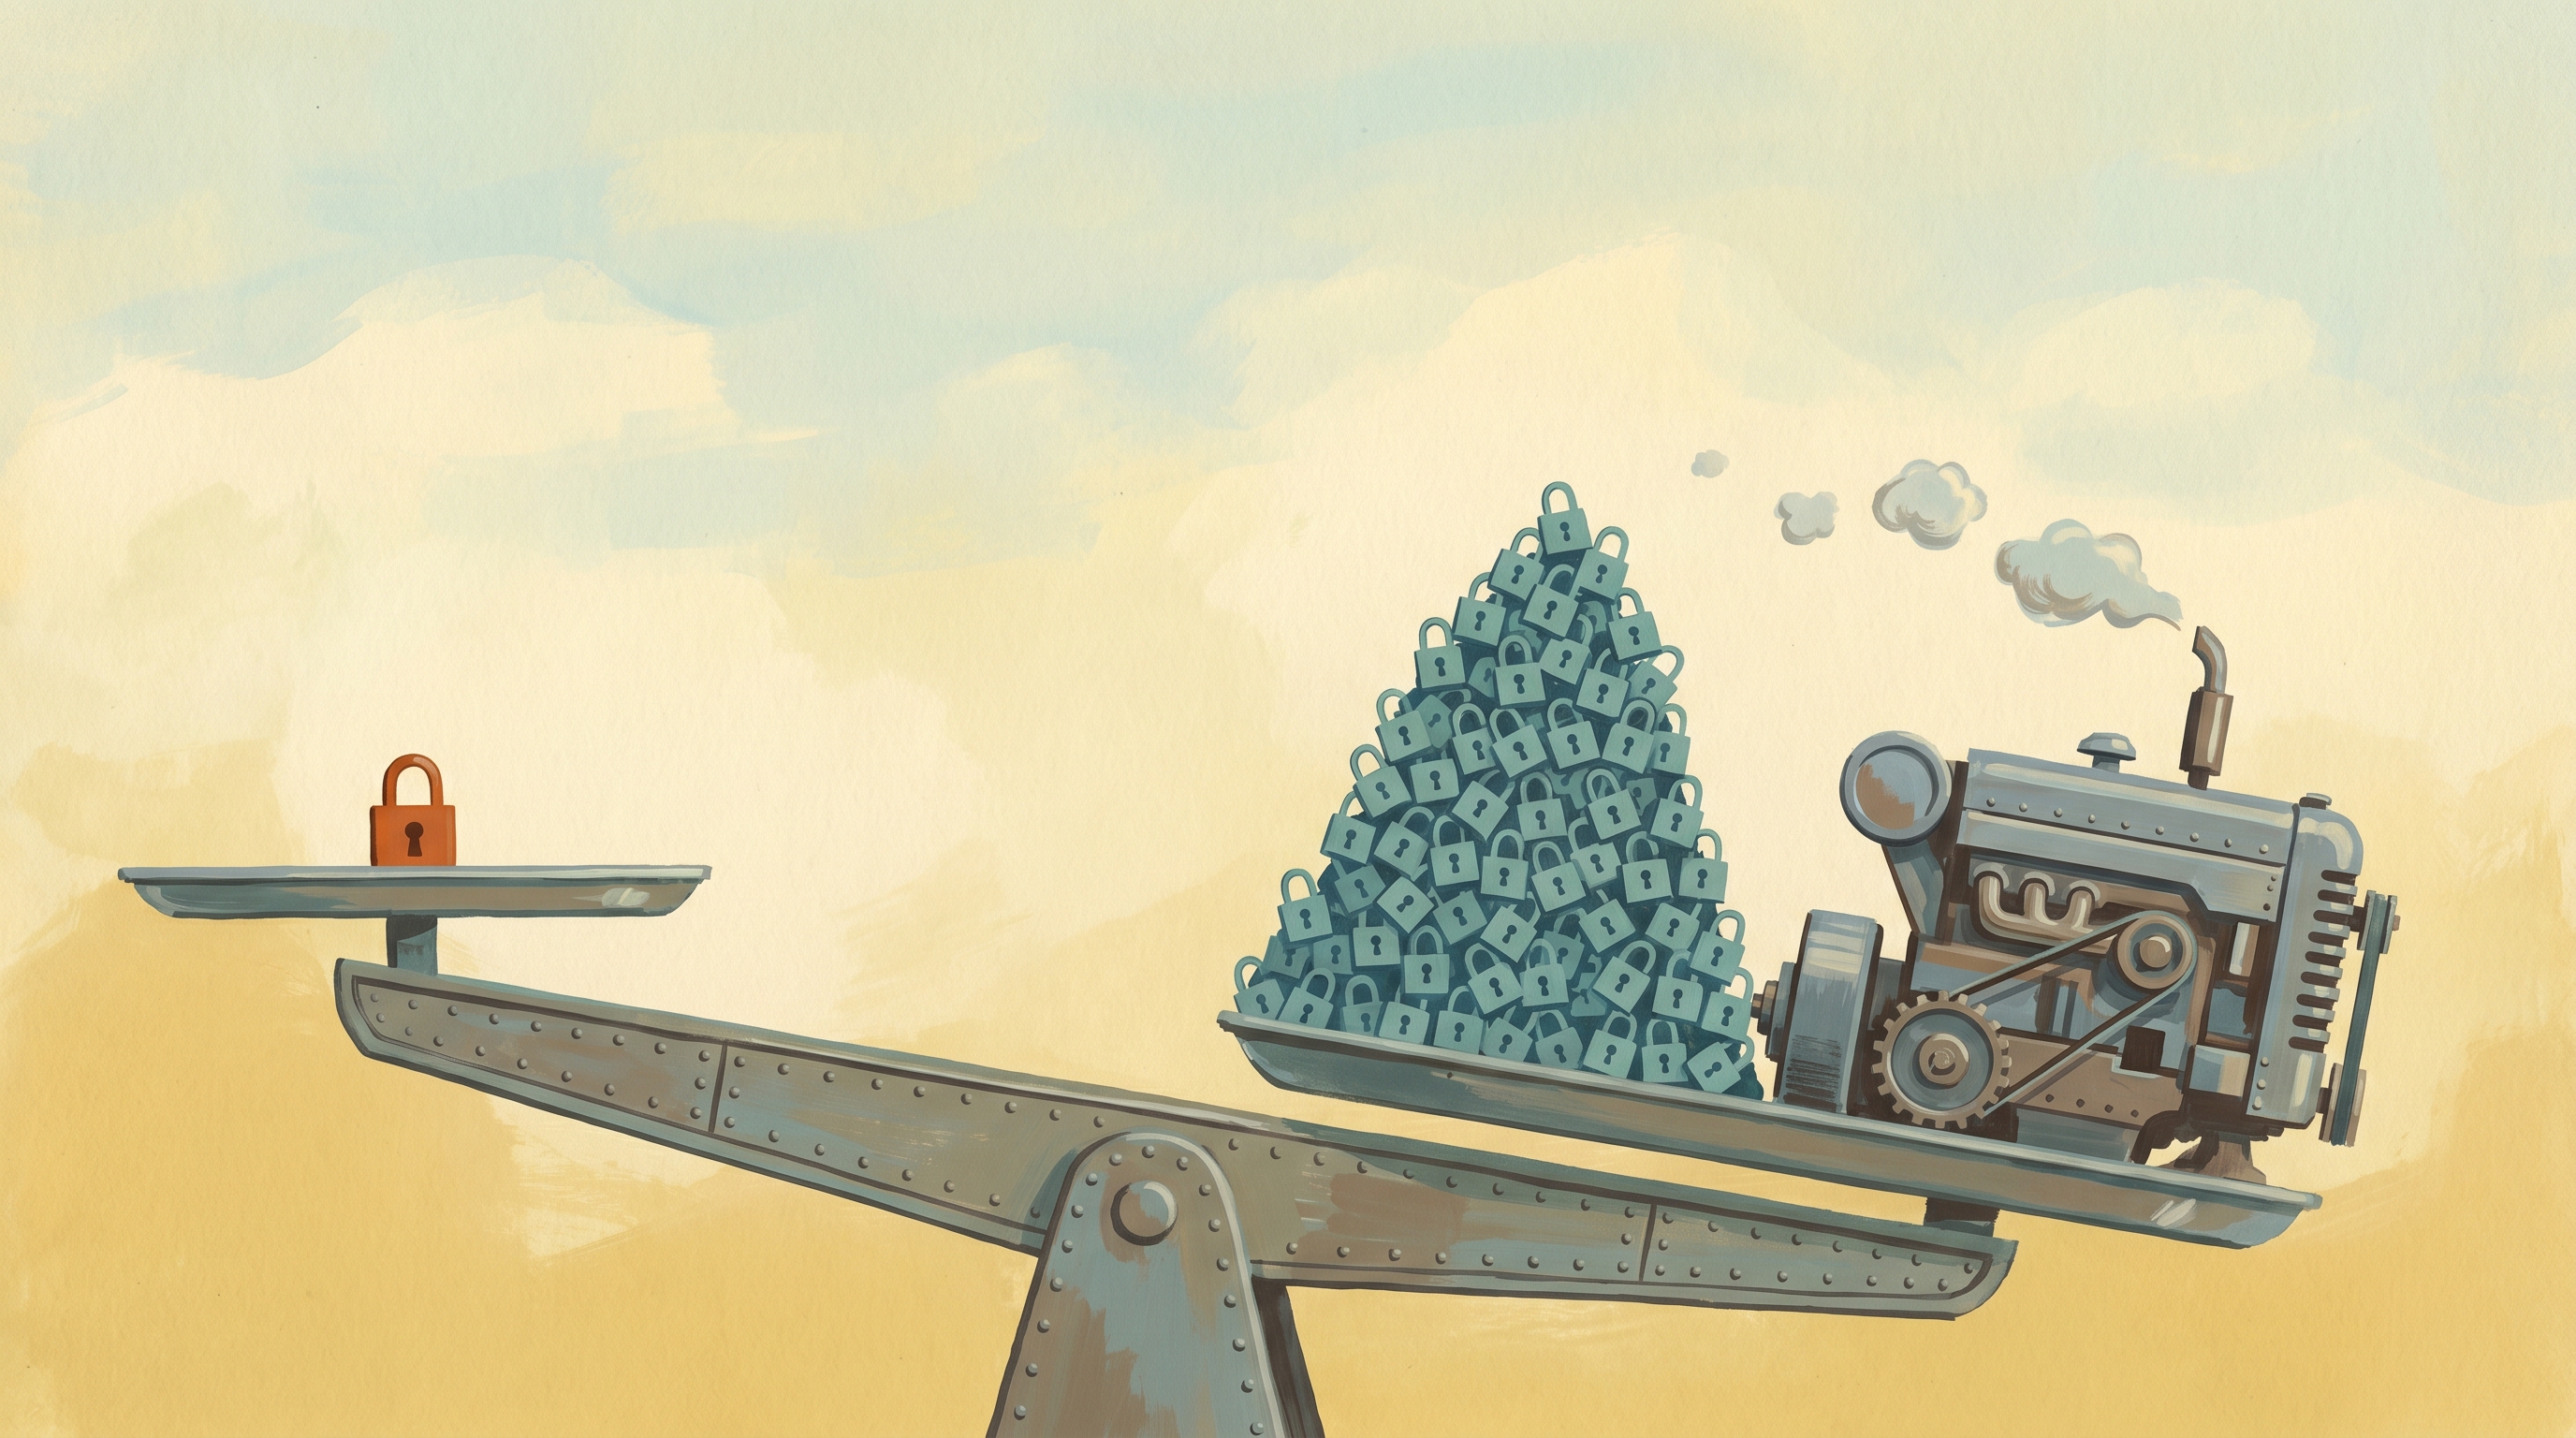
Every time someone questions the cost of pervasive encryption, the same citation gets wheeled out: Google's 2010 Gmail rollout, where TLS added "less than 1% of CPU load, less than 10 KB of memory per connection, and less than 2% of network overhead." It's in the IETF draft on TLS overhead. It's in conference talks. It's in vendor decks justifying mTLS-everywhere service mesh designs.
It's also fifteen years old and quietly misleading.
The Gmail number is true. It's just not generalisable. Google were terminating TLS on frontends with hand-tuned BoringSSL, AES-NI on every core, sessions that lived long enough to amortise the handshake, and engineers paid to shave microseconds. If your workload looks like that, congratulations — encryption probably is cheap for you too.
For everyone else, the picture is messier.
Bulk symmetric encryption is genuinely cheap when you have hardware acceleration. AES-NI turns AES-GCM into something close to memory bandwidth speed. Take it away — older ARM cores without crypto extensions, certain embedded targets, some VM configurations where the instructions aren't exposed — and throughput collapses by an order of magnitude. I've seen teams ship to edge hardware and discover their "free" TLS was eating 30% of a core.
Then there's the handshake. Short-lived connections — think serverless, Lambda-to-Lambda, or any system with aggressive connection pooling limits — pay full asymmetric crypto cost on every call. ECDHE plus a signature isn't catastrophic, but multiply it by a service mesh sidecar doing mTLS to twelve dependencies per request and the numbers add up. Istio benchmarks have shown sidecar latency overheads in the single-digit milliseconds, which is fine until your p99 SLO is 50ms.
And memory. "10 KB per connection" sounds trivial until you're a load balancer terminating two million concurrent connections. That's 20 GB of buffers before you've done any actual work.
None of this is an argument against encryption. Encrypt everything, by default, full stop. But stop pretending it's free. Budget for it. Measure it. Pick ciphers that match your hardware. Reuse sessions. Question whether you really need mTLS between two pods on the same node when the kernel already isolates them.
The honest position is: encryption is cheap enough to be worth it almost everywhere, and expensive enough that you should know what you're paying.